
Switzerland to Host IATA Cybersecurity Summit as Germany and Others Explore Aviation Data Protection for Travel
Updated
Published
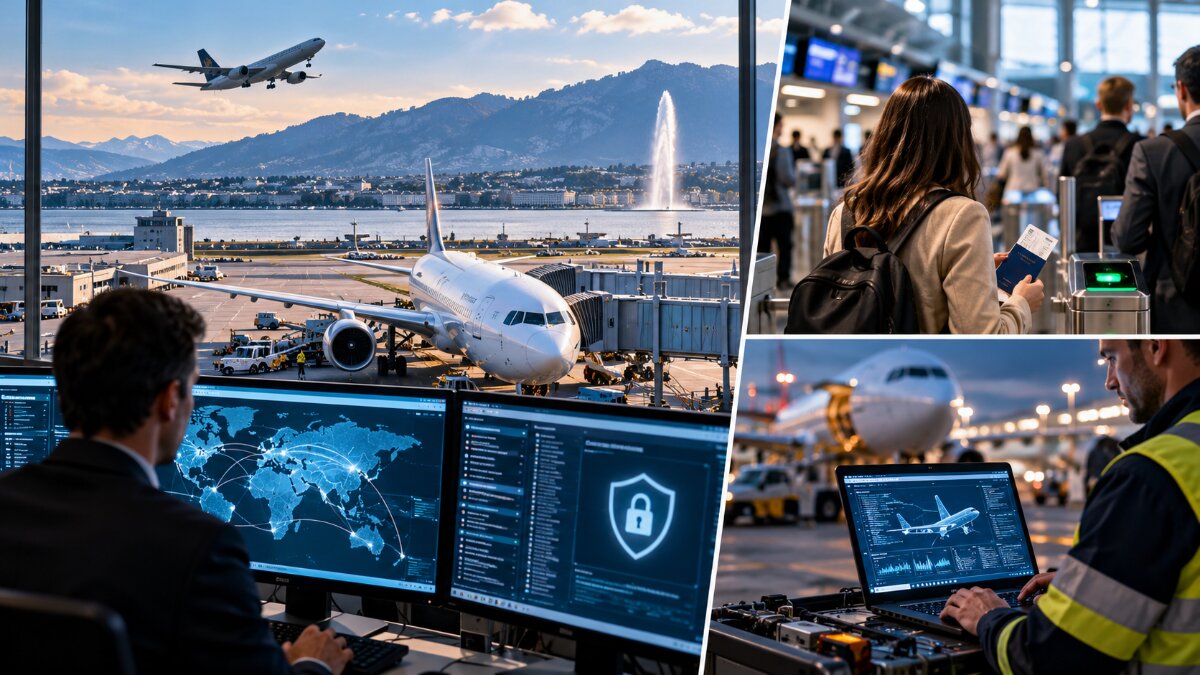
Switzerland will host the inaugural IATA Cybersecurity Summit in Geneva on 27–29 October 2026 as aviation organisations confront threats involving airline reservation platforms, airport customer information, connected suppliers and flight communications. Securing global aviation reveals a common international challenge: protecting passengers while keeping critical aviation services dependable. The meeting is scheduled, not concluded, and no five-country security agreement has been announced.
The International Air Transport Association (IATA) has scheduled the three-day gathering at its Geneva Conference Center, Route de l’Aéroport 33. Its published agenda covers artificial intelligence, supply-chain cyber defence, European information-security rules and recovery testing for airport equipment. The programme remains provisional.
Advertisement
Advertisement
For airlines and airports, the issue is whether flight information, customer records and essential ground services remain accurate and available when digital systems fail or face malicious interference. For agents, outages can also obstruct booking changes and customer support.
Five Countries Show How Aviation Cybersecurity Has Become a Shared Operational Priority
The countries are linked by different evidence, not a diplomatic alliance: Switzerland hosts, Germany tests, France regulates reporting, the UK has disclosed passenger-data exposure and the USA has audited flight communications.
Advertisement
Advertisement
| Country | Verified institutional development | Connection to travellers and aviation businesses |
|---|---|---|
| Switzerland | IATA summit on 28–29 October; FOCA guidance addresses aircraft, airport and passenger-data security. | Cross-border standards, system resilience and international industry coordination. |
| Germany | Lufthansa Group documented more than 650 penetration tests during 2025; EASA held a Part-IS workshop in Cologne on 7–8 October 2026. | Assurance for airline operations, contractors and technology infrastructure. |
| France | France’s DSAC issued March 2026 guidance on reporting aviation information-security events; Air France-KLM has documented booking and business-continuity risks. | Secure reservations, protected data and structured regulatory escalation. |
| United Kingdom | Manchester Airports Group reported an August 2026 customer-data incident, while the CAA reinforced cyber resilience in October. | Protection against phishing and misuse of airport-service customer information. |
| United States | A September 2026 GAO audit identified gaps in FAA monitoring and security assessments for aviation communications. | Integrity of air traffic information and protection against operational disruption. |
Switzerland Places Airport Infrastructure and Passenger Trust on the Geneva Agenda
The Swiss Federal Office of Civil Aviation treats cyber resilience as a matter of aviation safety, continuity and economic confidence. Its guidance covers aircraft systems, air traffic control, ground infrastructure and personal information. Its aviation oversight includes information-security requirements.
The gathering adds to Geneva’s business-events calendar, although verified delegate totals and local visitor-spending figures have not been provided.
Advertisement
Advertisement
Swiss guidance also addresses EASA Part-IS, which requires covered aviation organisations to manage relevant information-security risks systematically. For airports, the practical test is whether essential functions can continue safely if a connected system becomes unavailable. For travellers, resilience underpins reliable ground and flight services.
Germany Highlights Lufthansa Cyber Testing and Practical European Regulation
According to Lufthansa Group’s 2026 corporate governance presentation, the airline group conducted more than 650 penetration tests in 2025, expanding testing to aircraft-related and operational technology. It also reported a central AI-powered cyber-defence platform, information-security certification for core functions and greater scrutiny of suppliers.
These measure defensive testing, not successful attacks. At Geneva, Lufthansa-linked specialists are scheduled to address offensive AI, supplier vulnerabilities and global regulatory approaches, according to the official IATA programme.
Germany also hosted the EASA Part-IS implementation workshop in Cologne on 7–8 October. It examined implementation challenges.
France Strengthens Aviation Cyber Incident Reporting and Reservation-System Governance
France’s Direction de la sécurité de l’aviation civile, or DSAC, included Part-IS information-security reporting in its March 2026 guidance for aviation occurrence notifications. The associated government webinar materials identify a dedicated information-security occurrence category and explain reporting of incidents or vulnerabilities that may significantly affect aviation safety.
The French airline perspective is equally relevant. In its official universal registration disclosures, Air France-KLM identifies booking systems, revenue management, personal information and business continuity as interconnected operational risks. It describes redundancy, access controls and security assessment as safeguards.
Advertisement
Advertisement
These disclosures document exposure and controls; they are not evidence of a new confirmed breach. France links airline commerce with safety oversight.
United Kingdom Demonstrates the Difference Between a Data Incident and Airport Shutdown
On 27 August 2026, Manchester Airports Group disclosed unauthorised access affecting customer information related to airport parking, lounges, Fast Track and Wi-Fi registration at Manchester, London Stansted and East Midlands airports. Exposed categories included email addresses, telephone numbers, vehicle registrations and postcodes. The operator reported that bank or payment details were not held in the accessed system and that airport operations remained unaffected.
It concerns passenger information, not grounded aircraft. The UK Civil Aviation Authority’s 12 October update separately emphasised phishing risk after information exposure. It distinguished a September air traffic technology incident from intentional cyber activity.
The CAA’s cyber oversight framework encompasses aerodromes, flight operations, air traffic management and aviation security. Privacy and continuity require different responses.
United States Audit Exposes Risks Beyond Passenger Booking Platforms
The US Government Accountability Office report of 21 September 2026 identified weaknesses in the Federal Aviation Administration’s approach to aviation communications threats. The FAA supports more than 44,000 flights and three million passengers daily.
The GAO found incomplete risk assessments and limited real-time detection for some spectrum-related threats, including spoofing and jamming. It also examined vulnerabilities affecting ACARS and controller–pilot data-link communications, notably authentication and protection against message manipulation. Its nine recommendations address assessment, collaboration and stronger safeguards. The report did not establish that a successful cyberattack had compromised aircraft safety.
Advertisement
Advertisement
US airline representatives from United Airlines and Southwest Airlines are listed for the Geneva regulatory panel. Their participation connects regulation and airlines.
The Summit Programme Brings Airline Booking, AI and Airport Recovery Into Focus
The two-day IATA agenda connects cyber preparedness to flight-deck judgement, electronic flight bags, third-party suppliers, reservation technology and airport baggage systems. These planned discussions do not establish new incidents.
| Date | Planned discussion | Aviation risk under examination |
|---|---|---|
| 28 October | AI-enabled intrusion, flight-deck decision-making and electronic flight-bag protection | Integrity of operational information and human oversight. |
| 28 October | Passenger-data exposure claims, supplier dependencies and collective defence | Shared platforms, limited organisational visibility and incident coordination. |
| 29 October | EASA Part-IS, international regulations and airline representatives | Different compliance frameworks and consistent safety-focused controls. |
| 29 October | Human-supervised AI penetration testing involving booking, cargo and airport systems | Discovering weaknesses before operational disruption. |
| 29 October | Airport baggage-system recovery exercises and security operations | Validating backups, restoration procedures and continuity plans. |
The booking-system presentation is based on security-testing experience, not an announcement that reservation systems at the five featured countries have been breached.
EASA Part-IS Turns Digital Security Into an Aviation Governance Requirement
According to EASA, Part-IS became applicable to specified aerodrome and design or production organisations on 16 October 2025, followed by additional aviation organisations and competent authorities on 22 February 2026. Covered entities must identify relevant risks, detect incidents, respond appropriately and restore systems where aviation safety could be affected.
The Swiss regulator explains that this extends to information-security management systems, personnel responsibilities, access control and continuing oversight. The UK operates its own aviation cyber-oversight framework; its regulatory position should not be presented as identical to that of EU Member States. The USA likewise uses distinct federal responsibilities and aviation security requirements.
Shared suppliers still require clear reporting, escalation and continuity responsibilities.
Advertisement
Advertisement
Aviation Cyber Resilience Has Measurable Economic Stakes in 2026
The IATA June 2026 industry outlook projects 5.1 billion passengers, an 84% passenger load factor and US$23 billion in global airline net profit for 2026. The forecast net margin is only 2%, equal to approximately US$4.50 per passenger. These figures do not represent cyber losses.
| Verified 2026 indicator | Official figure | Why digital continuity matters |
|---|---|---|
| Global airline passengers, forecast | 5.1 billion | Huge volume of journeys depends on connected services. |
| Industry net profit, forecast | US$23 billion | Thin margins limit room for avoidable disruption costs. |
| Net profit margin, forecast | 2.0% | Recovery efficiency becomes strategically important. |
| EU cyber incidents involving transport in ENISA’s 2026 review | 8% of incidents recorded across sectors | Transport is a significant target, although this is not an aviation-only percentage. |
According to the European Union Agency for Cybersecurity, its September 2026 review covers incidents observed during 2025. It identifies transport among affected sectors and warns about interconnected digital dependencies. The figures cannot price a hypothetical aviation cyberattack.
Original Analysis: The Hidden Risk Lies Between Travel Systems
Aviation disruption is often measured in cancelled flights, but a narrower metric can miss the consequences for travel distribution. A traveller may retain a valid seat while losing access to an airport-service account. An agent may still see a reservation but be unable to complete a change if a supporting supplier fails. These are different failure modes, requiring different customer messages and different recovery decisions.
The five-country evidence exposes three separate layers. The UK’s airport data incident demonstrates confidentiality risk without a reported operational shutdown. The US audit examines integrity and availability in communications used for safe flight operations. Germany’s testing programme and France’s regulatory reporting framework demonstrate preventative controls and structured escalation. Switzerland supplies the setting for discussing how such systems interact.
A stronger resilience benchmark would therefore assess not just whether an organisation detects an attack, but whether its partners can still authenticate transactions, preserve booking records, identify affected passengers and restart critical functions safely. Travel sellers also need an evidence trail showing which instructions came from verified suppliers during an incident.
This is an editorial inference from primary-source evidence, not a finding announced by IATA. It shifts attention from headline breach counts towards the less visible interfaces where a local digital fault can become an international customer-service problem.
Advertisement
Advertisement
Critical Operational Takeaways for Travel Agents and Tour Operators
- Validate supplier alerts: confirm disruption notices through established airline, airport or booking-platform channels before changing itineraries.
- Preserve reservation records: retain permitted booking references, ticket status and contact histories in controlled systems with appropriate access permissions.
- Prepare manual escalation: agree with airlines and consolidators how urgent changes, traveller assistance and refunds will be handled if normal platforms are unavailable.
- Limit data exposure: restrict access to passenger information, apply multifactor authentication where available and watch for phishing following disclosed incidents.
- Test recovery arrangements: include airport-service suppliers, payment partners and technology providers in practical continuity exercises.
- Separate incident categories: distinguish suspected cyberattacks, confirmed personal-data exposures and ordinary technical faults before advising customers.
Global Aviation Growth Will Depend Increasingly on Tested Digital Resilience
The Geneva summit will not itself introduce new airline routes, universal travel rules or an international security treaty. Its longer-term significance rests on whether the industry advances coordinated testing, evidence-based oversight and recovery processes across airlines, airports and suppliers. Restoring services and trustworthy information will influence confidence and the reliability of international connections.
FAQs
When is the IATA Cybersecurity Summit 2026 taking place?
The scheduled dates are 28–29 October 2026, at IATA’s Geneva Conference Center in Switzerland. The event agenda may change before the meeting.
Are Switzerland, Germany, France, the UK and USA launching a joint cybersecurity agreement?
No five-country agreement is established. The countries share related security challenges.
Does the Geneva summit mean airline booking systems have been hacked?
No. The programme includes security testing of booking and connected aviation systems. That does not establish a breach.
Did the UK airport data incident stop flights?
Manchester Airports Group reported that its August 2026 customer-data incident did not disrupt airport operations or compromise aviation safety or security. Some customer contact and airport-service details were exposed.
What should travel businesses do about aviation cybersecurity risks?
Verify alerts, protect passenger data, review suppliers and rehearse rebooking and assistance during outages.
Advertisement
